
In many jurisdictions, including the EU, website owners are legally required to obtain cookie consent when collecting visitors’ personal data for third-party use.
However, if you’re not aware of applicable cookie consent requirements, you could expose yourself to legal liability for non-compliance.
In this article, we’ll cover everything you need to know about collecting cookie consent, including CCPA vs. GDPR, and provide a simple compliance checklist you can follow.
TL;DR – Cookie Consent Requirements
We recommend reading the whole article to understand how cookie consent works. But if you’re pressed for time, here’s a quick summary of what we discuss in this guide:
- The types of cookies that don’t require consent: authentication, user-input, user-customization, and security cookies
- The types of cookies that need consent: analytics, advertising, and social media
- GDPR requires website owners to collect cookie consent before storing third-party data, while CCPA doesn’t.
Keep reading for an in-depth review of cookie consent requirements, including their implications for website owners.

Which Cookies Require Consent (and Which Do Not)?
The requirement to collect cookie consent depends on the data you collect and the intended purpose. For example, cookies that collect your visitors’ data or offer more services beyond enhancing your website’s functionality require consent.
Essential cookies don’t require consent because they are necessary for your site’s main functioning. However, to build transparency and customer trust, explain to your visitors their primary function.
Let’s explore different types of cookies:
Cookies That Do Not Require Consent
Such cookies enhance a website’s functionality and deliver the services users request.
Examples include:
- Authentication Cookies: You should be able to prompt users on whether they want to remain logged in for security purposes.
- User-Input Cookies: Used to track users’ input on your website, such as filling out a shopping cart or promo code forms.
- User-Customization Cookies: Prompt visitors about their preferences, such as language or font size. However, consent may be required if the cookies collect personal data for UI personalization.
- Security Cookies: Enhance website security by prompting visitors after multiple failed login attempts.
Cookies That Require Consent
These cookies collect data about how your visitors interact with your website. They offer insights beyond improving website functionality, such as website analytics and marketing.
Examples include:
- Analytics Cookies: Used to track user browsing experience and purchasing journeys for insights into how to personalize visitors’ browsing experience.
- Advertising Cookies: They monitor customer behavior and collect visitor data for designing targeted marketing campaigns.
- Social Media Cookies: Placed by third-party social media platforms to enable content sharing and track user interactions.
GDPR Standards – The Gold Standard for Opt-In
General Data Protection Regulation (GDPR) sets the rules for how organizations can collect, process, and store data for people in the European Union (EU) and European Economic Area (EEA).
For website owners, GDPR requires user consent for collecting and processing your visitors’ data; otherwise, you risk financial and legal liability.
GDPR is the gold standard for opt-in privacy laws because it requires consent to be given freely, that users be informed, and that the rules be unambiguous.
Cookie Consent Requirements
Here are the main cookie consent requirements you must know for compliance:
- Active Opt-In: Consent must be explicit and easy to understand, such as clicking the “Accept” button or checking an empty box. One way to ensure active opt-in is by adding a cookie consent widget that appears when first-time visitors open your website.
- Easy Consent Withdrawal: Users should be able to revoke their consent easily. For instance, setting up a link that allows them to withdraw consent.
- Cookie Banner Transparency: Explain the main purpose of the cookies and any third parties involved in understandable language. Consider adding a tooltips widget to your website that provides additional information when visitors hover over a cookie type.
- Active Record Keeping: Record the users’ consent, including when you received it and the information provided, for audit purposes.
- Avoid Cookie Walls: Don’t manufacture consent by blocking your visitors’ access to your site if they opt out of data collection.
- No All-In-One Consent: Ask for consent for each cookie category, rather than a single all-encompassing solution.
- Avoid Pre-Ticked Boxes: Pre-ticked boxes are prohibited to avoid confusing users when giving consent.
Data Protection Principles
Follow these GDPR data protection principles when processing your visitors’ data:
- Lawfulness, Fairness, and Transparency: Inform users clearly why their data is required and how it will be used.
- Purpose Limitation: Process the data based on the intended purpose. For example, if you’re collecting data to enhance UX, don’t use it for targeted marketing.
- Data Minimization: Collect only the necessary information for the specified purpose.
- Accuracy: Ensure the collected information is precise and updated regularly.
- Storage Limitation: As the website owner, store the users’ information for the required time to fulfill the specified purpose, and then delete the data securely.
- Integrity and Confidentiality: Store the information securely to avoid data breaches and leaks.
Common GDPR Cookie Mistakes That Lead To Fines
Although GDPR is understandable, some website owners still make common mistakes that can trigger fines.
These errors include:
1. Not Recording the Consent Logs
As a website owner, you must prove that your website offers consent. Lack of accurate consent logs may lead to non-compliance issues, as you cannot confirm when consent was received.
Document all consent logs to ensure GDPR compliance, especially when under review for suspected misconduct, to avoid unnecessary penalties.
2. Collecting Data Before Consent
Consent must be established before collecting data. This, however, cannot happen retrospectively, meaning you cannot collect your users’ data and ask for permission later.
Under GDPR, this is a breach of the data privacy laws and will trigger non-compliance penalties.
3. Unclear Consent Banners
Placing unclear banners that are hard to understand, making it difficult to determine whether visitors consented, violates the GDPR standards.
Another instance would be failing to provide users with sufficient information about why consent is required, or complicating the consent process by placing pre-ticked boxes.
4. Failure to Include Consent Withdrawal
Not including a consent revocation solution triggers fines because you haven’t provided a way for users to opt out. Additionally, failing to simplify the withdrawal process may trigger penalties.
It’s important to note that data collected with consent is lawful, but processing a customer’s data after withdrawal of consent is illegal.

CCPA/CPRA & US State Laws – The Opt-Out Model
Several US states follow the California Consumer Privacy Act (CCPA) and its expansion, the California Privacy Rights Act (CPRA).
Unlike GDPR, the opt-out model allows businesses to collect customers’ data by default, as long as they have notified users and given them the right to revoke consent.
It’s important to note that while US states follow the opt-out model, the rules don’t apply uniformly across all states. Each state has different enforcement regulations and user privacy rights, so consult an expert for further clarification.
Key Requirements Under CCPA/CPRA
Cookie consent requirements under CCPA/CPRA include:
- Notice Before Data Collection: Inform users of the type of information you will gather before collecting any data.
- Provide an Opt-Out Option: Allow visitors to opt out easily and avoid confusing them with pre-ticked boxes.
- Data Minimization: Collect only the information you need to analyze visitor behavior, and nothing more.
- Data Retention Disclosure: Disclose how long you will keep the data to ensure transparency.
Consumer Rights Under CCPA/CPRA Regulations
CCPA/CPRA regulations require website owners to protect the following consumer rights:
- Right to Opt-Out: Provide an opt-out option that’s clear and easy to understand.
- Right to Know: Inform users about the information you collect, its intended purpose, and how it is used.
- Right to Delete: Delete collected information upon the user’s request to remain compliant.
- Right to Correct: Correct any information you have about the user upon request.
- Right to Limit: Use the collected information for the intended purpose only, especially when handling sensitive personal data, such as financial account information.
Side-By-Side Comparison of GDPR and CCPA/CPRA
The table below provides a side-by-side comparison of GDPR vs. CCPA/CPRA regulations:
| Feature | GDPR | CCPA/CPRA |
| Approach | Opt-in (Consent needed) | Opt-out (Right to stop collection of data) |
| Main Rights | Access, transparency | Know, delete, limit, and correct |
| Data Scope | Personal data | An individual’s personal information and household data |
| Protected Group | People currently in the EU | California residents |
GDPR and CCPA/CPRA are very similar in regulation, with the primary difference being how they apply to website visitors.
Cookie Compliance Checklist for Businesses
To remain compliant with GDPR, your website must move beyond simply notifying users that it uses cookies and adopt a transparent compliance system.
Follow this checklist to ensure total compliance:
- You have provided cookie definitions, including how the website uses them.
- You have categorized the cookies based on their intended purpose.
- You provide accurate details about the cookies, including their names, purposes, and durations.
- The consent banner is easy to understand and doesn’t have pre-ticked boxes.
- You provide clear, easy-to-understand instructions on how users can withdraw consent.
- The cookie policy is in bullet points, making it easy to read for all users.
- The cookie policies and consent banners are mobile responsive.
- The last update date is displayed, and you are tracking the changes.
- You review the cookie policy after 6 months or after significant website changes.
How to Build a Compliant System Using Webynize
A cookie consent widget helps you stay compliant and build trust with your website visitors. Designed with real-world compliance challenges in mind, Webynize helps website owners build a user-friendly, compliant system that adapts to GDPR and CCPA regulations.
This section provides step-by-step guides for creating a cookie consent widget and adding it to your website.
Creating a Cookie Consent Widget on Webynize
Follow these steps to generate an embed code using our widget:
- Sign up on Webynize to access our vast widget library.

- Click the +Create Widget button to access the widget library.
- Open the dropdown menu and select the cookie consent widget.

- Input a custom name for the cookie consent widget and click Next to open the customization panel.
- Draft the banner text that will appear on the consent widget and include a link to your resource section if needed.

- Navigate to the buttons, colors, and fonts tabs on the left and style the widget to your preference.

- Click Embed on Website and specify your web builder.

- Copy the embed code that appears on the pop-up.

Adding the Cookie Consent Widget to a Website
Next, let’s discuss how to add the widget to your website:
- Log in to your website admin dashboard.
- Open the web page where you want to add the cookie consent widget. We recommend adding the widget to the footer, so that it appears on all web pages.
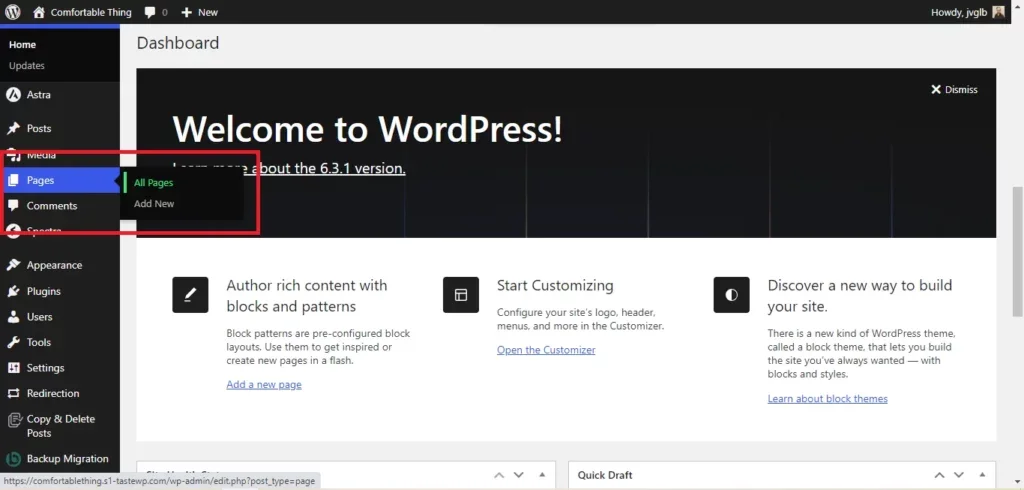
- Launch the code editor or rich text editor, depending on your website type.
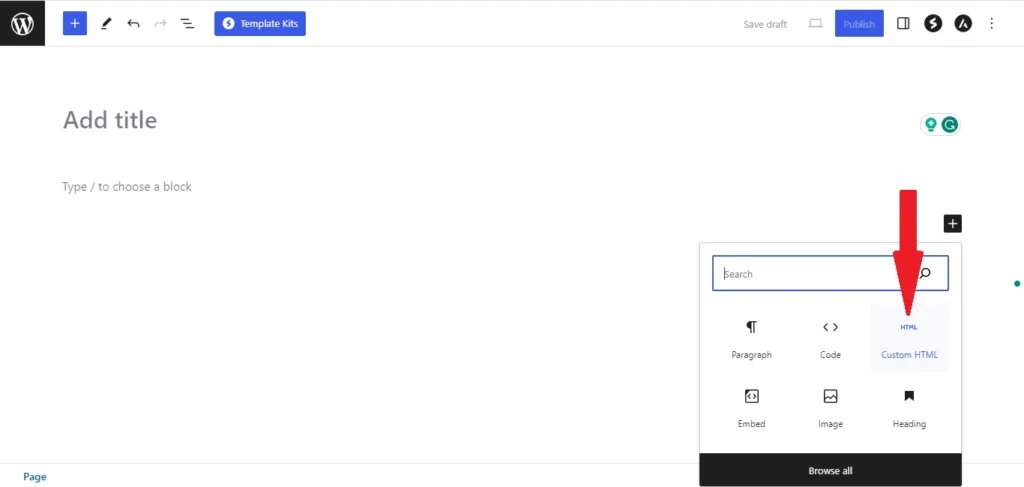
- Paste the embed code and save the settings.
Our Webynize widget is compatible with all major web builders, including Webflow, Wix, HTML, and Squarespace, meaning you can use the same cookie consent widget across your websites.
Additionally, the widget is easy to implement and doesn’t require advanced technical expertise to set up and customize.
Create a cookie consent widget to enhance your website’s transparency and trust.
Frequently Asked Questions (FAQs)
Below are the most commonly asked questions about cookie consent requirements:
Can Cookie Consent Affect Website Speed?
Yes. Cookie consent widgets can affect website speed if they require loading additional JavaScript files.
However, lightweight cookie consent widgets are optimized for speed, improving load times and UX.
Do All Countries Require Cookie Consent?
No. Not all countries require cookie consent, but many do.
For example, all EU member states must obtain consent before storing visitors’ data.
Are There Exceptions for Essential Cookies?
Yes. Essential cookies are exempt from consent requirements because they help in the website’s functionality. Examples include remembering items in the cart, enabling fraud prevention, and keeping visitors logged in.
However, explain these essential cookies to your visitors and what they do to ensure transparency.
Can Users Revoke Consent Easily?
Yes. GDPR rules require website owners to allow users to revoke consent easily.
For example, you could provide a cookie settings link that users click to unsubscribe automatically.
How Often Should Cookie Policies Update?
You should update your cookie policies every 6 to 12 months to ensure compliance with privacy regulations, such as GDPR and CCPA.
Additionally, update your cookie policies after significant changes to your website, or if there are privacy regulation changes in your target countries.
Conclusion
GDPR and CCPA were introduced to prevent businesses from collecting users’ personal data without consent.
However, compliance goes beyond displaying the cookie consent banner; the policy should use plain language and provide clear instructions on where users can opt in or opt out. Additionally, you must disclose the information you intend to collect and how you’ll use it.
The best way to ensure GDPR/CCPA compliance is by using a website widget that lets you collect visitors’ consent easily when they load your website.
Developed by veteran developers behind SociableKIT, our Webynize cookie consent widget offers easy plugin implementation and doesn’t require you to write any code. Additionally, our widget is mobile-optimized, providing a seamless user experience across devices.
Create a cookie consent widget today to ensure your website remains compliant.


